detecting automated session cookie replay attacks by analyzing low-level browser timing anomalies
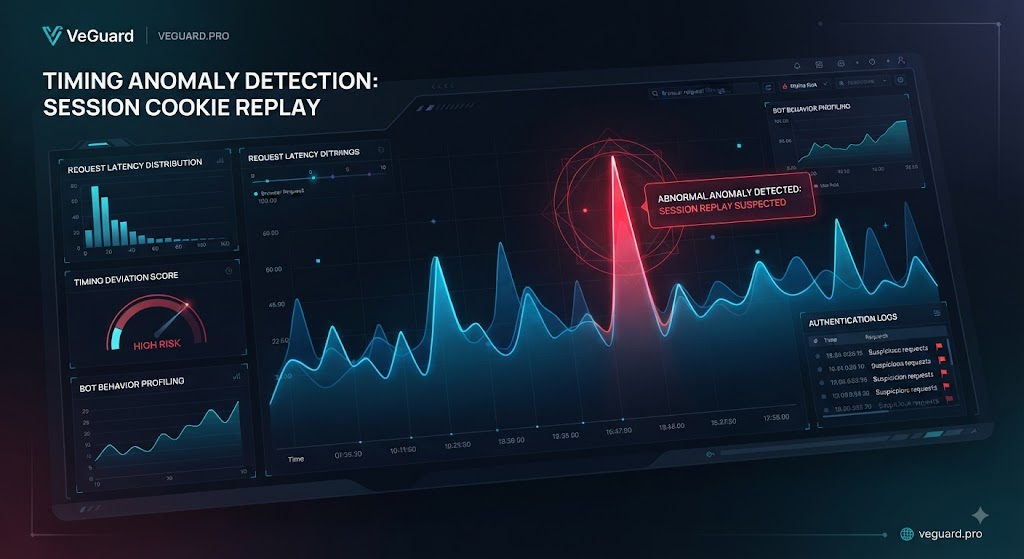
Catching the Phantom: How Browser Timing Anomalies Expose Session Cookie Replays
Authentication security has evolved significantly, yet session hijacking remains one of the most stubborn vectors facing web applications. When an attacker manages to steal a valid session cookie through XSS or infostealer malware, they can replay that token to impersonate a legitimate user. Traditional security tools often fail here because the token itself is technically correct. To stop them, you need to look beyond the cookie.
The Limits of Token-Only Validation
Most applications validate sessions purely on the presence and cryptographic signature of a cookie or JSON Web Token (JWT). If the token checks out, the request is granted. Attackers know this, which is why session replay has become a preferred method for bypassing multi-factor authentication and standard login screens. Once inside, they have full access to user data, billing details, and sensitive application functions.
Unmasking Replay Attacks Through Client Environment Timing
Even when an attacker successfully clones a cookie, the execution environment where that cookie is replayed almost never matches the original browser instance. Factors such as hardware execution cadence, DOM rendering intervals, and low-level event loop timings create distinct temporal fingerprints. veguard.pro analyzes these subtle microsecond browser timing anomalies at the edge.
When a request arrives with a valid session token but an aberrant timing profile indicative of automated replay or a foreign device, veguard.pro flags or blocks the session instantly. This provides a crucial layer of defense that does not rely on user friction or constant re-authentication.
Secure Your Sessions with veguard.pro
Stopping session hijacking requires moving security deeper into the client-server handshake. By integrating veguard.pro into your application stack, you add robust device and environmental awareness that identifies sophisticated replay attempts in milliseconds. Protect your user base and eliminate unauthorized session takeovers today.
Ready to upgrade your authentication security? Visit veguard.pro to get started.
🌐 veguard.pro