how to audit your web app for missing security headers in 5 minutes using browser developer tools
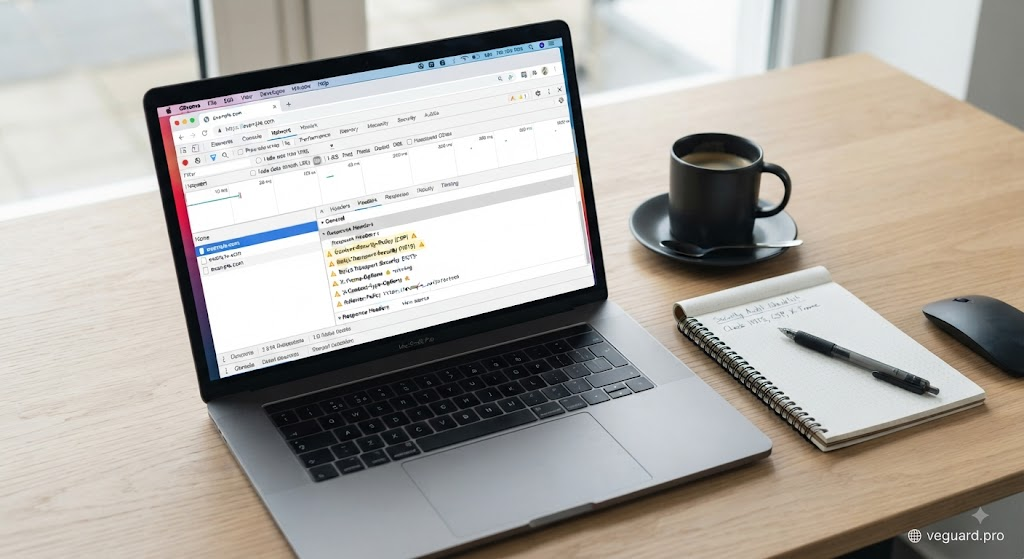
How to Audit Your Web App for Missing Security Headers in 5 Minutes
When building and scaling web applications, engineering teams often pour hundreds of hours into business logic, database optimization, and user experience, while basic infrastructure hygiene slips through the cracks. One of the simplest yet most overlooked security practices is verifying your HTTP response headers.
Today, we are sharing a quick, actionable tip you can execute in less than five minutes using tools already installed on your machine to uncover immediate security gaps.
Step 1: Open Your Developer Tools
Launch your favorite modern browser, navigate to your web application, and press F12 (or right-click anywhere and select Inspect) to open the Developer Tools panel. Head straight to the Network tab.
Step 2: Isolate the Root Request
Hard-refresh your page (Ctrl+F5 or Cmd+Shift+R) to capture all initial assets. Click on the very first request in the list—usually matching your domain name—which represents the primary HTML document returned by your server.
Step 3: Inspect the Response Headers
Look at the Headers sub-tab and scroll down to the Response Headers section. You are looking for critical headers that instruct the browser on how to handle your content securely. Are headers like Content-Security-Policy (CSP), Strict-Transport-Security (HSTS), X-Content-Type-Options, and X-Frame-Options present? If any of these are missing, your application is unnecessarily exposed to clickjacking, MIME-type sniffing, and cross-site scripting risks.
Next Steps for Advanced Protection
While checking response headers is a fantastic baseline sanity check, modern web applications face sophisticated automated threats, headless scrapers, and device spoofing that standard header policies alone cannot stop. To truly safeguard your app, you need real-time visibility into incoming device signatures and behavioral trust metrics.
Protect your user flows from automated abuse today. Head over to veguard.pro to discover how seamless edge device intelligence can fortify your infrastructure without adding friction for legitimate users.
Call to Action
Run your 5-minute header audit today, patch any missing defenses, and visit veguard.pro to supercharge your application security stack.
🌐 veguard.pro