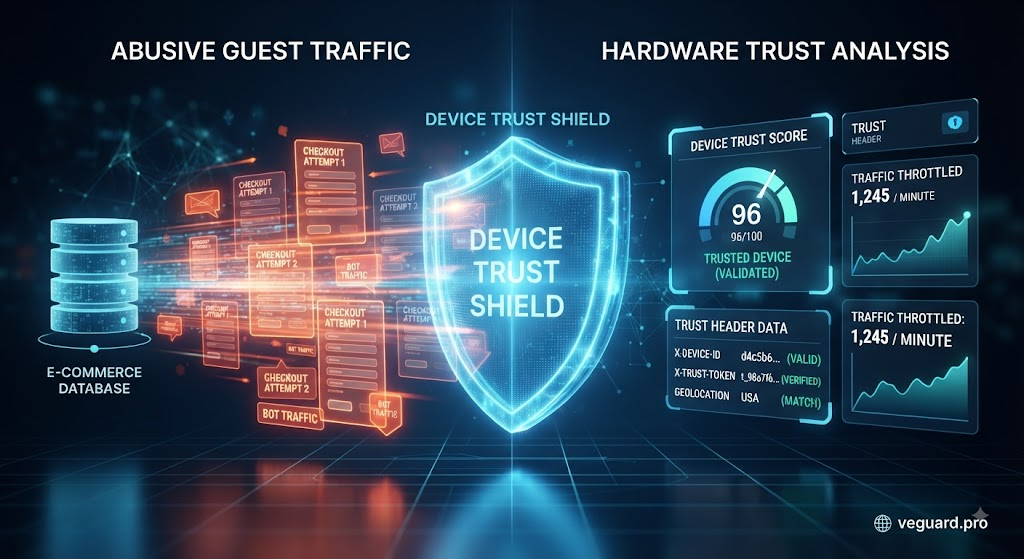
how to use device trust headers to instantly throttle abusive guest checkout attempts before they hit your database
Stop Guest Checkout Abuse Today Using Device Trust Headers
If you run an e-commerce platform or digital service with a guest checkout feature, you have likely dealt with automated checkout spam, credential stuffing, or inventory hoarding. Traditional defense mechanisms typically rely on IP rate limiting. Unfortunately, modern bots easily bypass IP blocks by rotating through vast residential proxy networks. Today, we look at a quick, actionable tactic you can implement to stop these attacks before they impact your infrastructure.
The Problem with IP-Centric Defenses
When malicious actors target a guest checkout flow, they rarely use a single IP address. They distribute their requests across thousands of endpoints, making standard IP-based rate limiting ineffective. If your rate limiter is too strict, you risk locking out legitimate shoppers who share a corporate network or public Wi-Fi. If it is too lenient, bots slip through and disrupt your operations.
The Actionable Solution: Edge-Level Device Trust
To solve this, you need to shift your verification layer to the edge and evaluate hardware-level signals rather than network addresses. When a visitor loads your guest checkout page, veguard.pro computes a robust device trust signature based on low-level browser and hardware attributes.
By checking these trust headers before your application server executes a single database query, you can:
- Instantly identify emulated browsers and automated scripts.
- Throttle suspicious high-velocity checkout attempts silently.
- Preserve lightning-fast page speeds for genuine human buyers.
Getting Started Today
Integrating device intelligence into your checkout pipeline takes minutes, not weeks. Stop wasting engineering hours cleaning up fraudulent orders and database clutter. Head over to veguard.pro today to secure your checkout flows with real-time edge device intelligence.
🌐 veguard.pro