myth: changing your user agent string is enough to disguise an automated browser
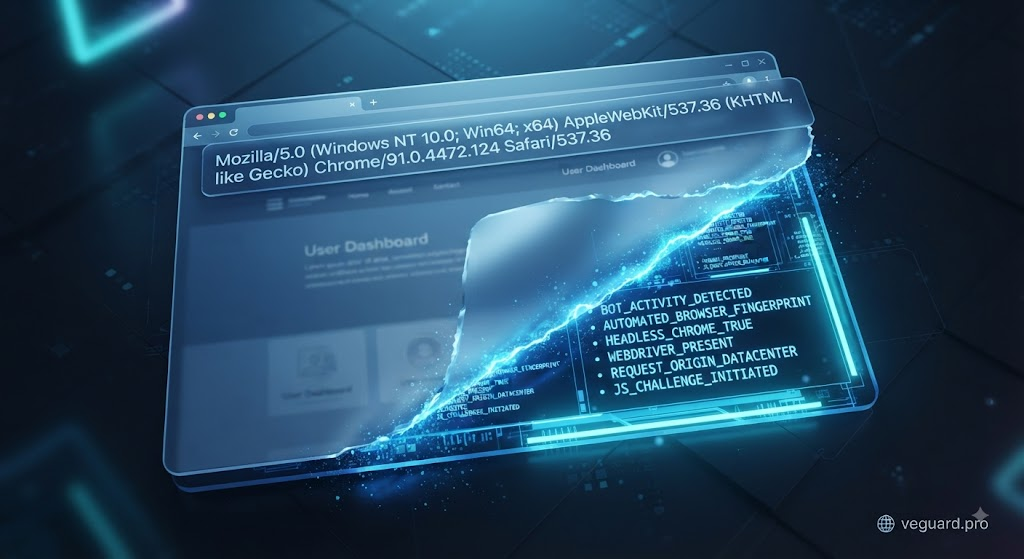
The User-Agent Illusion: Why Header Tweaks Fail Against Modern Defense
For years, a persistent misconception has floated around web development and security forums: the notion that if an automated script or scraper alters its user-agent string to mimic a standard desktop browser, it becomes indistinguishable from a legitimate human user. While this rudimentary tactic might bypass poorly configured rate limiters or legacy log analyzers, it offers zero protection against modern threat actors utilizing sophisticated automation frameworks.
Beyond the Surface: What User-Agents Miss
A user-agent string is merely a self-reported HTTP header. Any script can claim to be the latest version of Chrome running on Windows or Safari on macOS. Relying on this header for security is akin to trusting a visitor's nametag without checking their ID. Sophisticated scrapers, credential-stuffing bots, and automated checkout rings routinely rotate user-agent strings, yet they invariably leave distinct fingerprints deeper down in the browser runtime environment.
Revealing the Hardware Footprint
True device intelligence looks past what the browser says it is and measures what the browser actually does. Factors such as WebGL and canvas rendering variations, audio context generation quirks, hardware clock skews, and memory allocation patterns reveal the true underlying environment. An automated browser running headless in a cloud data center will inevitably betray its artificial origin through execution timing anomalies and missing native platform hooks, no matter how pristine its user-agent header looks.
Securing Your Endpoints with veguard.pro
Eliminating automated abuse requires moving past fragile, surface-level rules. veguard.pro integrates directly into your pipeline at the network edge, mapping raw runtime signatures and hardware characteristics into dynamic trust scores. Stop guessing who—or what—is visiting your application.
Ready to upgrade your endpoint security? Discover veguard.pro today and secure your platform against advanced automation.
🌐 veguard.pro