myth: increasing rate-limiting thresholds or implementing standard ip-based blacklisting provides adequate protection against modern distributed botnets
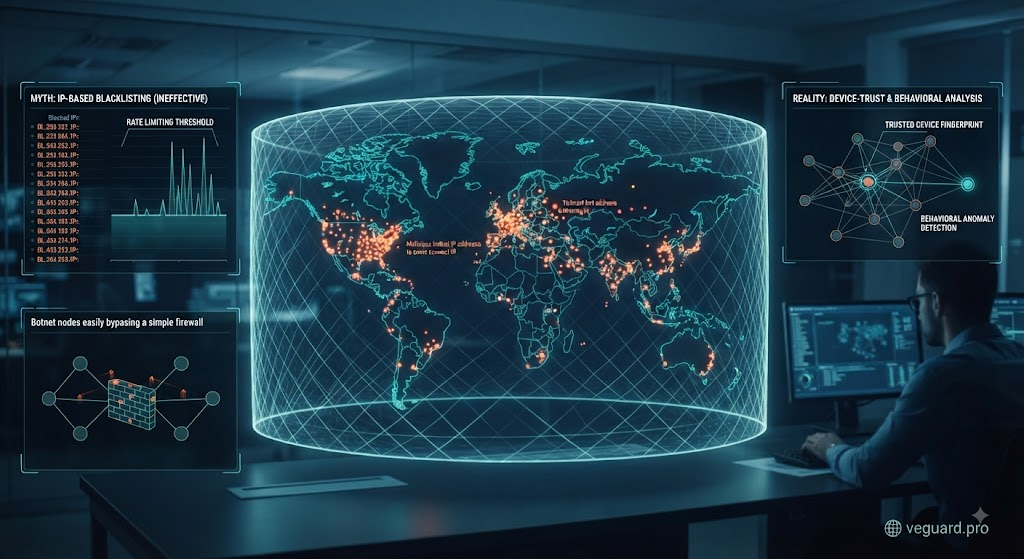
The Death of IP-Based Security: Debunking the Rate-Limiting Myth
For decades, the frontline defense for web applications has been straightforward: if an IP address makes too many requests, block it. If a known malicious traffic source emerges, add it to the IP blacklist. It is a simple concept that has guided web security architecture since the early days of the internet. But in today's threat landscape, relying solely on IP-based rate limiting is like locking your front door while leaving the windows wide open.
Modern distributed botnets have evolved far beyond static infrastructure. Attackers routinely leverage massive residential proxy networks, routing millions of automated requests through legitimate consumer IP addresses. To a traditional web application firewall (WAF), these requests look entirely human. The result? Engineering teams spend countless hours maintaining brittle blocklists while genuine users face frustrating friction or get caught in collateral-damage lockouts.
Why IP-Based Blacklisting Fails Today
The fundamental flaw of IP-based security is that IP addresses identify network locations, not entities or devices. When an automated script or headless browser farm rotates through ten thousand proxy IPs in an hour, standard rate-limiting thresholds either trigger false positives for shared corporate networks or fail to catch distributed scraping loops entirely.
Furthermore, maintaining custom regex rules and IP blocklists creates an unsustainable operational burden. Every time your engineering team patches one leak, the botnet shifts its proxy pool, restarting the cycle of midnight alerts and performance degradation.
Shifting from Network Perimeters to Device Trust
True security requires looking past the transient network layer and evaluating the actual device posture of the client. By examining low-level hardware telemetry, browser execution footprints, and cryptographic device bindings, security systems can accurately distinguish between genuine users and sophisticated automation regardless of what IP address they happen to be routing through.
Securing Your Infrastructure with veguard.pro
veguard.pro eliminates the guesswork of perimeter defense by introducing dynamic, hardware-bound behavioral trust policies. Instead of reacting to fluctuating IP addresses, veguard.pro analyzes foundational device signals at the network edge, blocking automated attacks instantly before they consume backend database resources or drain valuable inventory.
Stop fighting an endless battle with outdated IP blocklists. Empower your engineering team with autonomous device intelligence and secure your web ecosystem today. Visit veguard.pro to get started.
🌐 veguard.pro