protecting high-stakes freelance milestone payouts from compromised developer devices
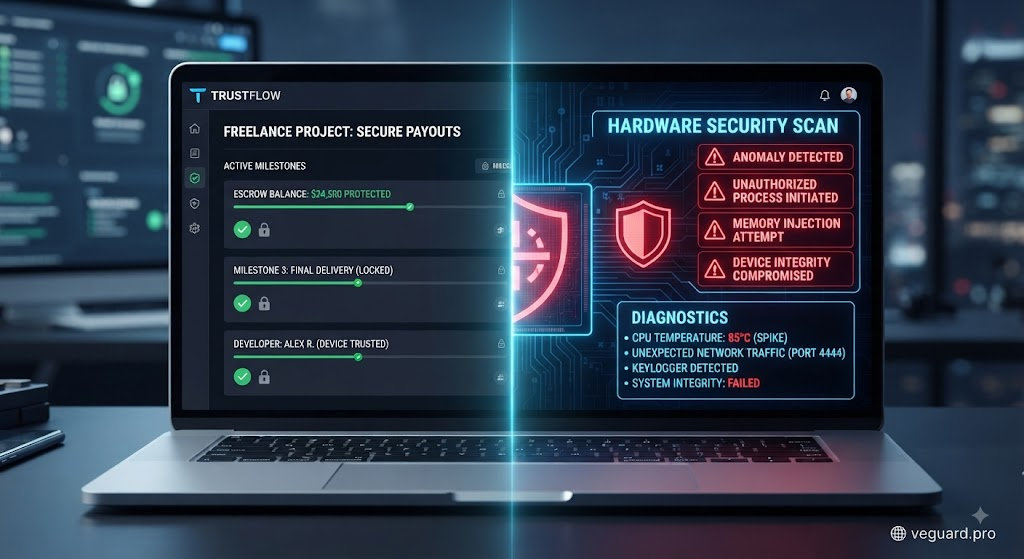
Securing High-Stakes Freelance Milestone Payouts Against Compromised Devices
The freelance economy thrives on trust. Platforms bridge clients and independent talent across the globe, holding milestone funds in escrow until code is delivered and approved. But as the stakes rise—with single projects frequently crossing five figures—these platforms have become prime targets for sophisticated account takeover (ATO) attacks.
Traditional defenses like passwords and MFA often fall short. If a developer falls victim to an info-stealing malware strain that logs in via a trusted browser session, traditional security tools see a familiar face. The result? Unauthorized milestone payouts routed directly to an attacker's wallet.
The Gap in Traditional Auth
When dealing with financial transactions, verifying who is logging in is no longer enough; you must verify what device they are using. Attackers frequently harvest session tokens from legitimate machines and replay them from foreign, untrusted environments.
Hardware-Bound Trust with Vegaurd.pro
Vegaurd.pro solves this by embedding runtime hardware intelligence directly into your authentication and payout validation layers. Instead of relying solely on IP addresses or easily spoofed headers, veguard analyzes low-level hardware characteristics—such as CPU execution quirks, hardware clock skew, and browser runtime anomalies—to instantly flag unauthorized environments.
Preventing Financial Leakage
By requiring hardware verification before high-value escrow actions are authorized, marketplaces can block attackers even if they possess valid credentials and cookies. This ensures that every dollar released goes strictly to the verified developer's trusted workstation.
Conclusion
Protecting platform liquidity and user trust is essential for scaling a digital workforce. Implement veguard.pro today to secure your milestone workflows and eliminate compromised-device payout fraud for good.
🌐 veguard.pro