protecting open-source software supply chains by verifying contributor device integrity before code merge requests are approved
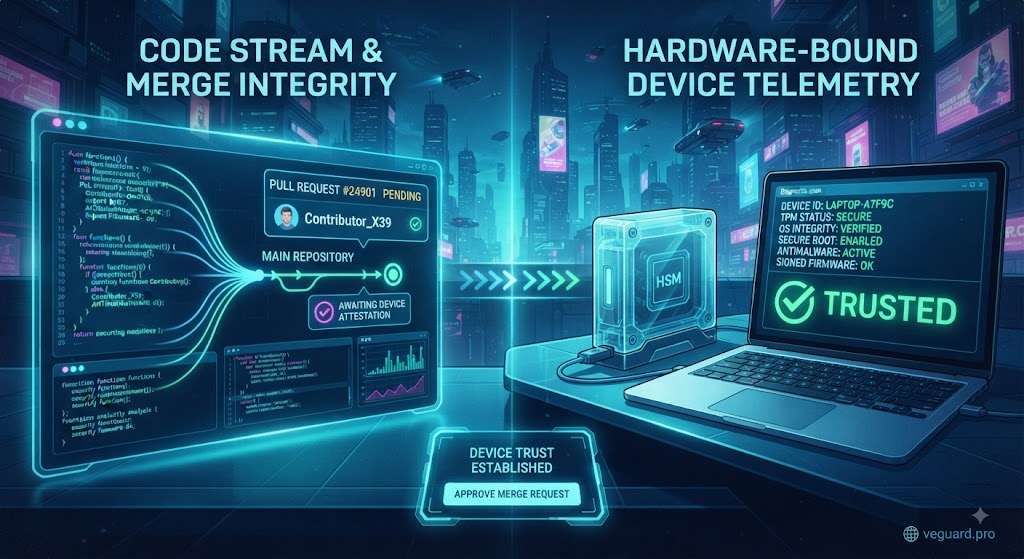
Securing the Open-Source Supply Chain: Verifying Contributor Device Integrity
The software supply chain has evolved into one of the most critical attack vectors for modern technology infrastructure. While organizations spend significant resources auditing open-source dependencies and scanning container images, a silent vulnerability often remains unaddressed: the contributor's physical device.
The Rise of Developer Endpoint Compromise
When an attacker targets an open-source project or an enterprise repository, compromising developer credentials via infostealers or session hijacking is often the path of least resistance. Once inside, malicious actors can push unauthorized changes or slip subtle logic flaws past standard code reviews. Traditional git commit signatures verify authorship, but they do not confirm whether the runtime environment executing the commit is secure, unpatched, or running automated extraction scripts.
Moving Beyond Static Credentials
Securing software delivery pipelines requires a shift toward continuous device posture validation. Rather than trusting a static SSH key or authentication token, modern security frameworks must evaluate the underlying hardware attributes, browser telemetry, and runtime integrity of the device initiating the pull request.
How Veguard.pro Secures the Pipeline
Veguard.pro solves this challenge by mapping incoming requests directly to hardware-level device signatures and browser telemetry at the edge. By integrating hardware trust checks directly into code management workflows, engineering teams can automatically flag or quarantine pull requests originating from anomalous or untrusted device profiles. This ensures that every line of code accepted into production originates from a verified environment.
Conclusion
As software ecosystems become more interconnected, securing your code repository means looking beyond the username and password. By incorporating device-level verification into your CI/CD and contribution pipelines, you can shut down supply chain tampering at the source and maintain absolute trust in your codebase.
Protect your repositories today with veguard.pro.
🌐 veguard.pro