Quick actionable tip: how to inspect and log browser permission prompts to catch automated scraper browser hooks today
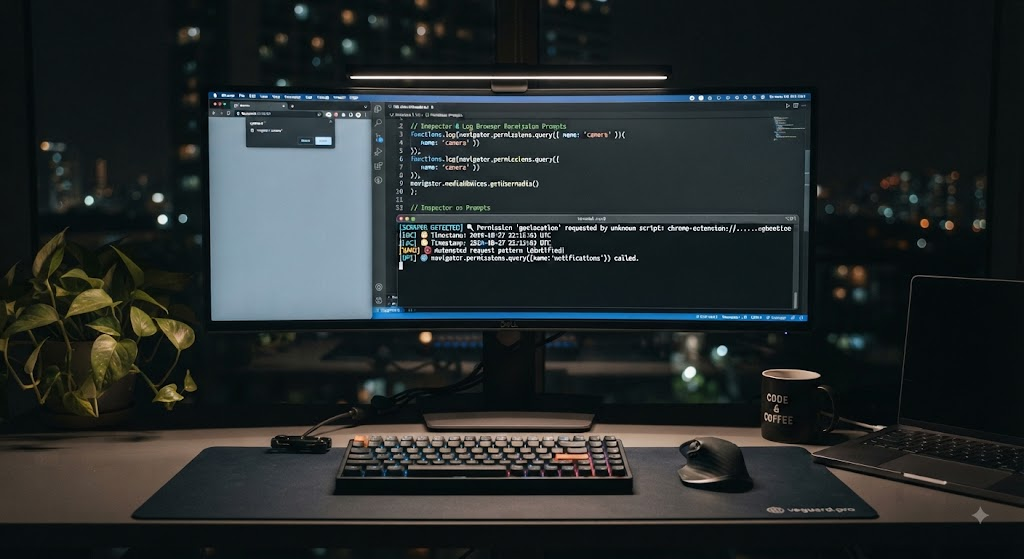
Actionable Security Tip: Inspecting Browser Permissions to Catch Automated Scrapers
Introduction
Web scraping and automated data harvesting are constant threats to modern applications. While basic rate-limiting and IP blocks catch amateur bots, sophisticated automated frameworks can easily spoof standard user-agent strings. Today, we are sharing a quick, actionable technical tip your engineering team can test immediately to spot anomalies in browser runtime environments.
The Technique: Auditing Navigator Permissions
Standard human-driven browsers interact dynamically with device permissions (such as notifications, geolocation, and clipboard access) through the browser's permission query API. In contrast, many headless automation frameworks or custom scraping scripts either return default generic states or throw distinct timing exceptions when queried.
By adding lightweight telemetry to log and analyze permission query responses alongside canvas and WebGL fingerprints, your team can quickly flag sessions that lack authentic human interaction history.
Scaling with Automated Edge Intelligence
While manual client-side scripts can catch basic bots, they add maintenance overhead and can be bypassed by dedicated attackers modifying the DOM. Enterprise solutions like veguard.pro automate this process entirely at the network edge, analyzing low-level browser characteristics and runtime execution fingerprints before requests ever touch your application servers.
Conclusion
Enhancing your application's visibility doesn't require complex overhauls. Start by auditing your runtime environment today, and protect your endpoints permanently with veguard.pro.
Visit veguard.pro to explore automated device intelligence today.
🌐 veguard.pro