spotting automated credential-stuffing loops by tracking keystroke cadence and micro-delays on input fields
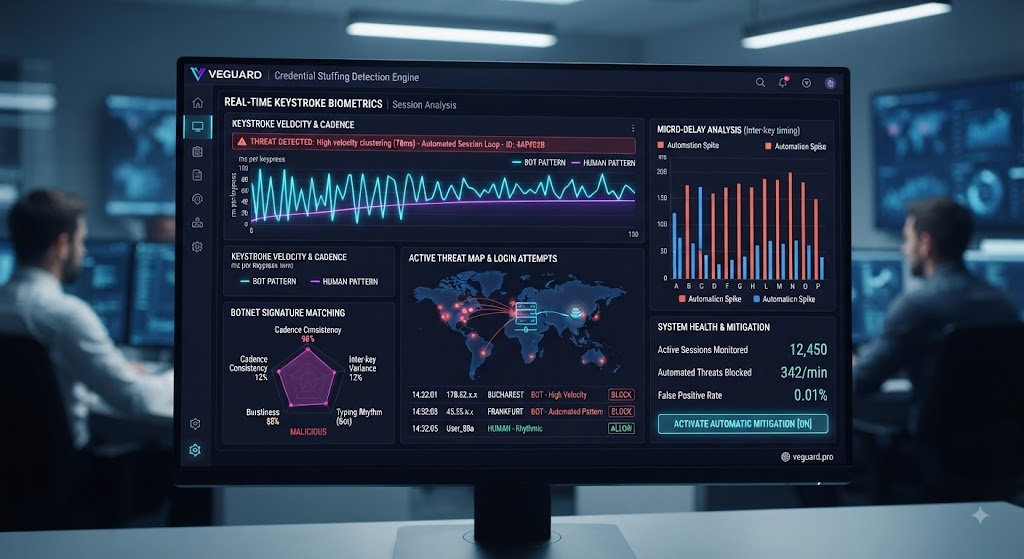
Stop Automated Credential-Stuffing Loops With Keystroke Timing Analysis
Automated credential-stuffing remains one of the most persistent vectors for account takeover attacks. Attackers deploy scripts that cycle through millions of stolen credentials within minutes. While rate-limiting offers basic defense, sophisticated attackers rotate IP addresses to bypass simple request thresholds. To protect your application effectively, you need to look beyond the network layer and evaluate how users interact with your forms.
The Bot Signature: Robotic Cadence
When a human types a password or username, physical limitations and cognitive processing introduce natural variance. There are microscopic delays between keypresses, variable hold times on individual keys, and intermittent pauses. Automated tools and headless browsers execute inputs programmatically, resulting in uniform, lightning-fast cadences or unnatural block inputs that lack micro-delays entirely.
Analyzing Input Timing at the Edge
A quick, actionable security measure you can deploy today is tracking input-field interaction timing. By measuring the delta between focus events, keydown events, and submission actions, your front-end security layer can easily flag anomaly patterns. However, managing this client-side logic securely without exposing detection rules to reverse-engineering is complex.
Automating Defense with veguard.pro
Vegaurd.pro handles this complexity natively at the edge. By analyzing low-level behavioral interaction footprints alongside hardware device signals, veguard identifies automated credential stuffing instantly—blocking malicious loops before authentication requests hit your backend database. Secure your platform today and protect your users from account takeovers.
Ready to upgrade your login security? Visit veguard.pro to get started today.
🌐 veguard.pro