The Great Security Migration: The Old/Manual Way vs. veguard.pro's Automated Device Intelligence
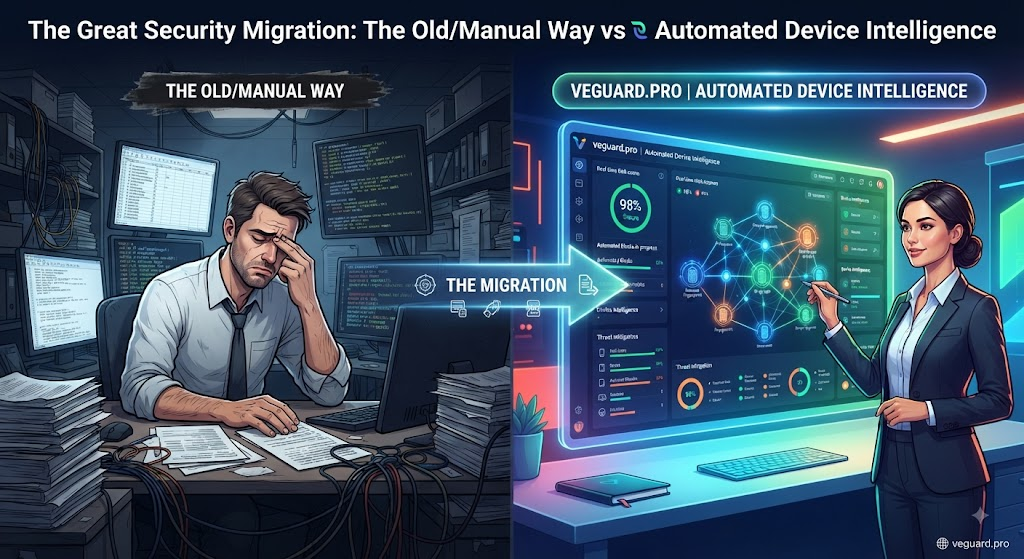
The Great Security Migration: Why Manual Fraud Rules Are Failing Engineering Teams
For nearly every digital product, SaaS platform, and high-traffic e-commerce site, security begins as an ad-hoc chore. When suspicious traffic or abuse starts ticking upward, teams reach for the tools they know: they block a malicious IP address, write a quick regex filter for a suspicious user-agent string, or set up a rudimentary rate limit.
While this manual approach feels productive in the short term, it creates a heavy operational drag. Let's look closely at how the traditional manual security model stacks up against modern, automated device intelligence with veguard.pro.
The Trap of the Manual Security Routine
In the old manual paradigm, security is reactive. Fraudsters, scrapers, and credential-stuffing bots act first, and your team responds later after reviewing logs or customer support complaints.
- IP Whack-a-Mole: Modern bad actors rarely stay on one IP address. They rotate through thousands of residential proxies and VPN nodes. Blocking an IP address today often means blocking a legitimate corporate subnet or a traveling customer tomorrow.
- Engineering Tax: Every minute your developers spend updating blacklist rules, auditing fake signups, or investigating suspicious logs is time stolen from building core product features.
- High False Positives: Static rules lack context. They treat an incognito user or a frequent network-switcher with the same suspicion as an automated script, creating friction for genuine customers.
The veguard.pro Way: Intelligent Edge Automation
veguard.pro replaces brittle heuristics and manual blacklists with hardware-level device intelligence. Instead of asking what network a visitor is on, veguard examines hundreds of subtle browser, canvas, WebGL, and hardware parameters to establish persistent device trust.
- Zero-Latency Edge Defense: Decisions happen instantly at the network edge via lightweight scripts that execute before authorization tokens are issued or forms are processed.
- Immunity to IP Shifting: Clearing cookies, switching browsers, or jumping across proxy IPs doesn't reset a device's risk profile. veguard recognizes the underlying hardware fingerprint.
- Reclaimed Engineering Hours: By automating risk assessment and removing the need for manual rule updates, your team can redirect focus entirely toward product growth.
Conclusion
Continuing to fight modern automated threats with manual IP maintenance is like using a paper map for a high-speed highway. Moving to veguard.pro equips your architecture with autonomous, device-level foresight.
Ready to eliminate manual fraud wrangling? Visit veguard.pro to see how easy automated edge defense can be.
🌐 veguard.pro