the rise of passkey adoption and why hardware-bound device posture validation is the critical missing layer for true passwordless security
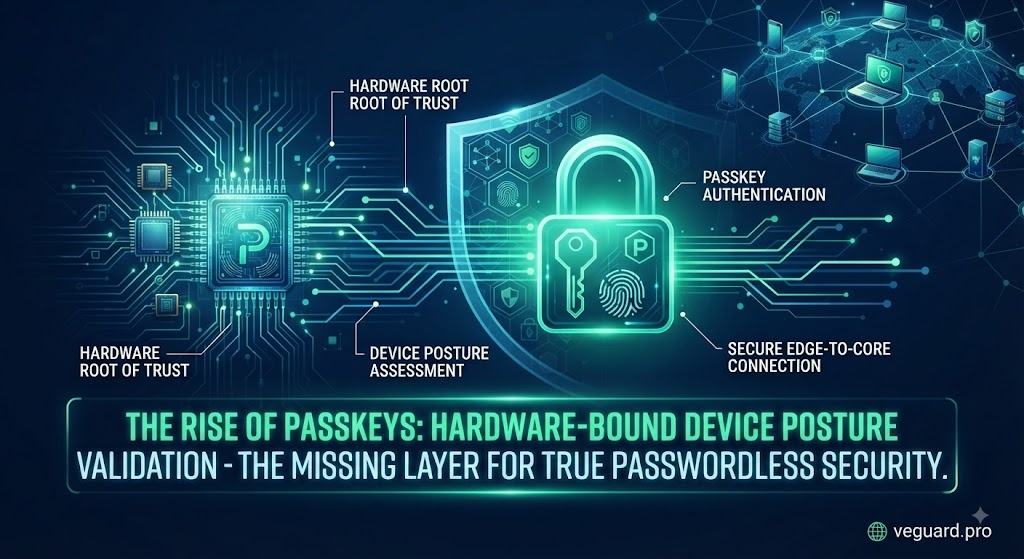
The Missing Link in Passkey Security: Why Device Posture Validation Matters Now More Than Ever
The software industry's migration toward passwordless authentication is moving at breakneck speed. Passkeys—backed by FIDO2 standards and webauthn primitives—are rapidly replacing traditional passwords across enterprise applications, fintech platforms, and consumer SaaS. Organizations are celebrating the death of the credential stuffing attack and breathing a collective sigh of relief.
However, as security teams lean heavily into passkey adoption, a dangerous blind spot is being overlooked.
The False Sense of Security in Passwordless Flows
Passkeys solve a massive problem: they eliminate phishing and weak passwords by binding user authentication to cryptographic key pairs stored locally on a device. When a user logs in, their device signs a challenge, proving possession of the private key.
Yet, a fundamental question remains unanswered: How do you know the device holding that passkey is trustworthy at the moment of login?
If a user's machine is running compromised firmware, infected with persistent background session stealers, or operating within an unauthorized virtualized emulator farm, the passkey can still be invoked or hijacked by malicious actors who have gained local execution control. Passkeys authenticate credentials, but they do not automatically audit device health or runtime integrity.
Bridging the Gap with Edge Device Intelligence
To achieve true zero-trust security in a passwordless world, authentication must combine user credential verification with continuous device posture assessment. This is where veguard.pro transforms your security stack.
Veguard.pro operates at the network edge, intercepting requests before authorization tokens or passkey challenges are finalized. By measuring low-level hardware telemetry—such as CPU clock skew, canvas signatures, and runtime environment characteristics—veguard.pro instantly validates whether the connecting hardware is genuine, untampered, and operating in a clean state.
Securing the Future of Authentication
As passkeys become the default standard for modern web apps, pairing them with dynamic hardware-bound trust policies is no longer optional for high-security platforms. Don't let a compromised endpoint undermine your passwordless architecture.
Integrate veguard.pro to add real-time hardware posture validation to your login pipelines. Visit https://veguard.pro to get started today.
🌐 veguard.pro