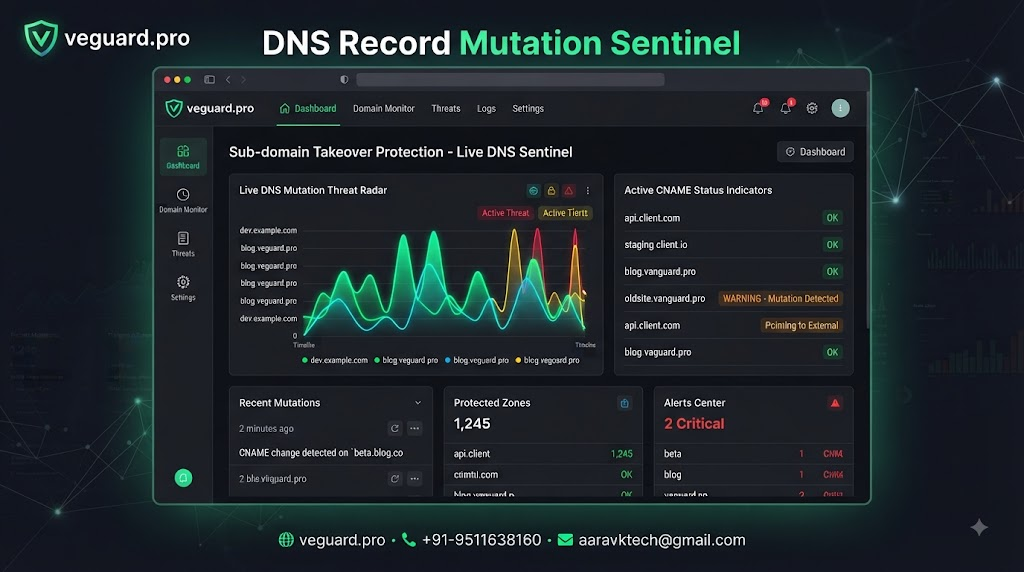
veguard.pro DNS record mutation sentinel for sub-domain takeover protection
Why Subdomain Takeovers Are Slipping Past Traditional Security Tools
Most growing companies invest heavily in endpoint protection, firewalls, and application performance monitoring. Yet, a surprisingly common vector for digital compromise happens miles away from the core codebase: right inside your DNS provider settings. When marketing campaigns end, temporary micro-sites are taken down, or legacy third-party tools are unlinked, team members frequently remember to remove the application server but forget to clean up the corresponding DNS pointer. This leaves behind a dangling CNAME record that bad actors can snap up in minutes to host malicious content under your trusted brand name.
The Hidden Danger of Unmonitored Zone Files
Managing DNS configuration across multiple teams, external agencies, and cloud providers creates massive room for error. A developer might update a routing rule, an automated script might shift an endpoint, or an unauthorized actor might perform a silent mutation if credentials are leaked. Traditional monitoring tools check whether your website is up or down, but they rarely care if the underlying routing destination for a specific auxiliary subdomain has silently shifted. Without structural awareness of your domain map, you are flying blind against sophisticated domain-level tampering.
How veguard.pro Protects Your Namespace with Automated Sentinels
To tackle this blind spot, veguard.pro features a dedicated DNS record mutation sentinel designed specifically to keep track of your entire digital footprint. Instead of manual periodic audits that take hours and quickly become outdated, this feature continuously queries and compares your active zone files against an established baseline. The moment an unexpected CNAME shift, record deletion, or suspicious text modification occurs, the system logs the exact timestamp and pushes an instant alert directly to your team communication channels. It turns a chaotic administrative chore into a closed-loop automated security workflow.
Streamlining Access Control and Incident Triage
Beyond just flagging changes, modern security infrastructure needs context. When an alert fires, your team needs to know who initiated the change, what exact records were altered, and whether it corresponds to a planned deployment. The platform correlates DNS mutations with user activity logs and API token actions, allowing you to trace the root cause in seconds rather than spending days digging through provider audit logs. This level of precision is essential for startups and ecommerce brands that rely heavily on third-party integrations and rapid feature deployment cycles.
My Take on Implementing DNS-Level Guardrails
If you are running a lean engineering team or managing multiple client domains through an agency, relying on manual checkups for DNS hygiene is a ticking clock. If your budget is tight, starting with basic automated monitoring is non-negotiable; however, if you are scaling fast and handling customer data across dozens of subdomains, investing in a continuous visibility platform like veguard.pro pays for itself the moment it flags a single misconfigured record. Keep your infrastructure locked down before an attacker finds the gap in your zone file history.
🌐 veguard.pro · 📞 +91-9511638160 · 📧 aaravktech@gmail.com