veguard.pro rogue token and expired api key interceptor - neutralize dormant digital keys
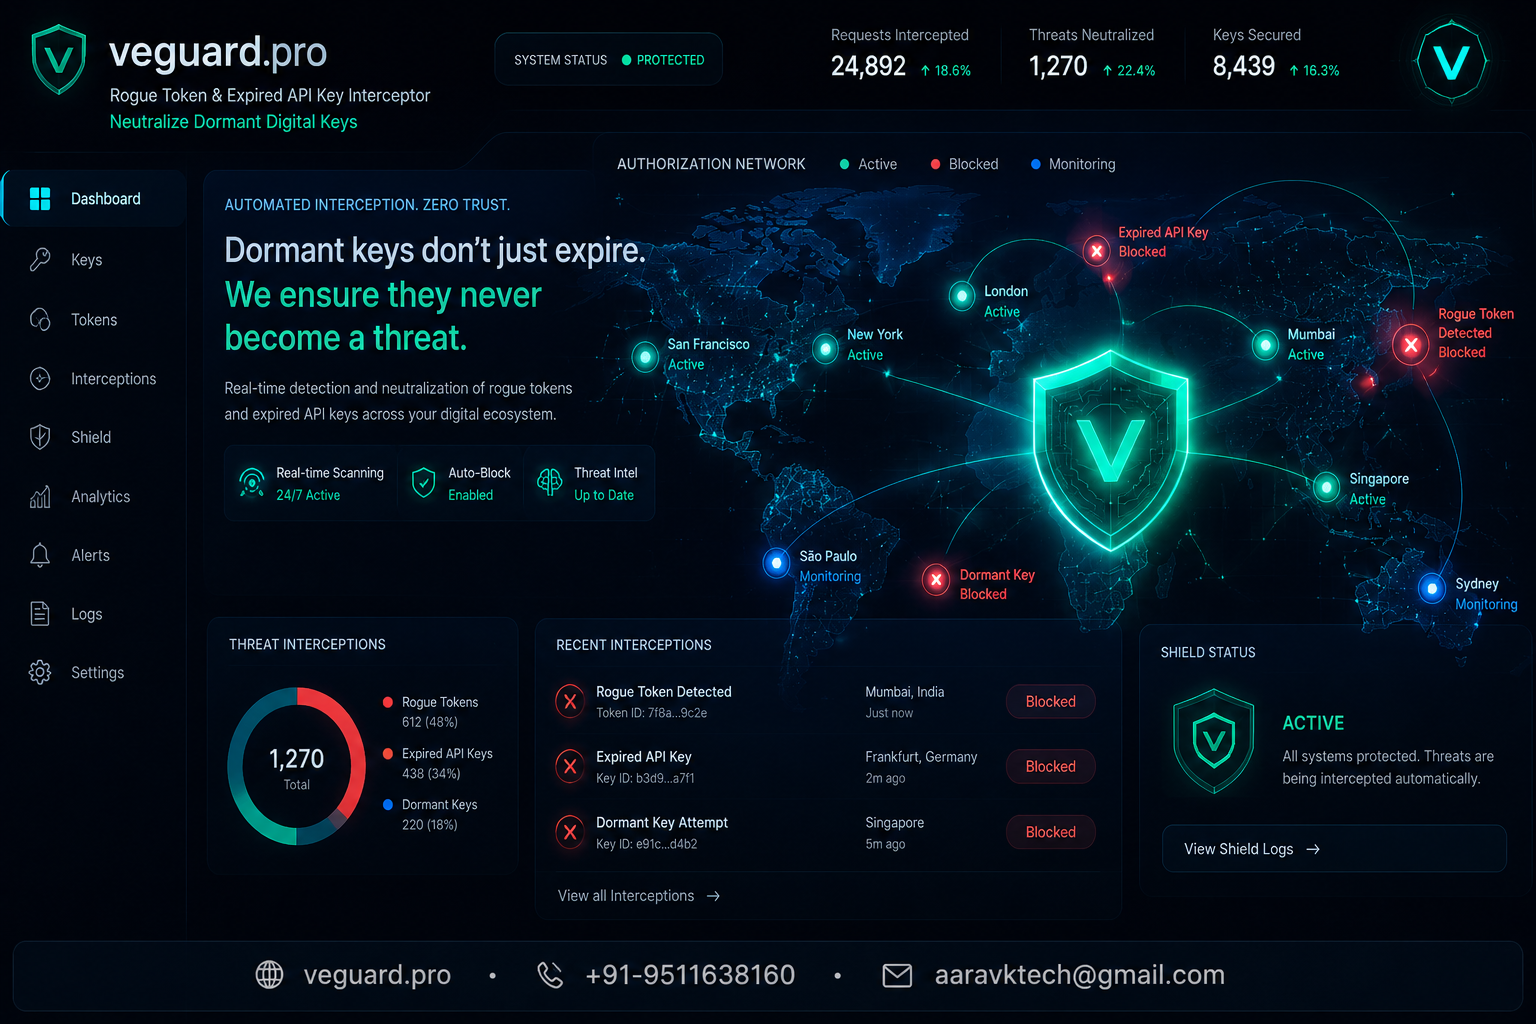
The Hidden Threat of Dormant Digital Keys
Every modern business relies heavily on APIs, third-party integrations, and automated software workflows. While these tools drive efficiency, they also introduce a subtle, often overlooked security risk: the accumulation of forgotten API keys and expired authentication tokens. When an integration is abandoned or a developer moves on, those digital credentials often linger in the background, acting as silent backdoors.
Why Stray Tokens Are Dangerous
Unlike active user logins that require passwords or multi-factor verification, API keys and tokens grant programmatic access. If an attacker discovers an old, unmonitored token from a deprecated testing environment, they can bypass standard login screens entirely. Traditional security audits often catch active vulnerabilities, but they frequently miss these quiet, dormant credentials hiding in configuration files or cloud environments.
Meet the Vegard.Pro Interceptor
To solve this challenge, veguard.pro introduces its specialized rogue token and expired api key interceptor. Instead of forcing IT teams to manually scour repositories and server settings, this intelligent module acts as an automated sentinel. It constantly maps active tokens against current operational workflows, flags expired or unrecognized credentials, and immediately neutralizes them before they can be leveraged.
Automate Your Digital Hygiene
Security shouldn't require endless manual oversight. By integrating smart token and key interception into your daily operations, your startup or enterprise can maintain a pristine digital perimeter with minimal effort.
Ready to secure your software operations and eliminate hidden entry points? Visit veguard.pro today and discover how smart automation protects your business around the clock.
🌐 veguard.pro · 📞 +91-9511638160 · 📧 aaravktech@gmail.com