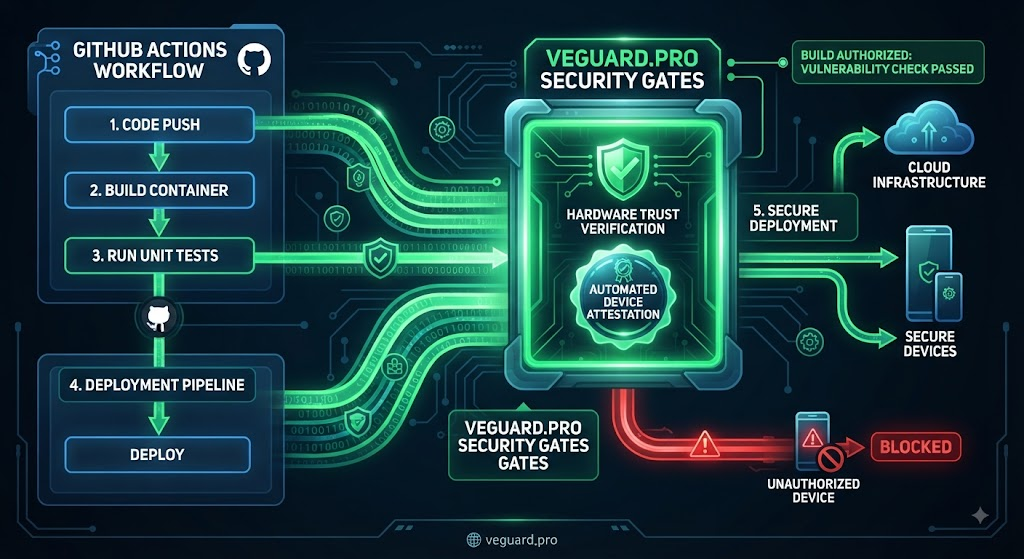
how veguard.pro integrates natively into github actions and CI/CD pipelines to block vulnerable or unauthorized device builds before deployment
Automating Security: How to Integrate Vegaurd.Pro Directly Into Your GitHub Actions Pipeline
For modern engineering and DevOps teams, security cannot be an afterthought tacked on at the end of a sprint. To maintain rapid release velocity while protecting against automated threats and unauthorized build environments, security checks must live where developers live: right inside the CI/CD pipeline.
Integrating veguard.pro into your workflow allows engineering teams to automate device-level trust verification seamlessly, ensuring that every deployment, endpoint connection, and developer API interaction is cryptographically backed by hardware intelligence.
Why Pipeline-Level Security Matters
Traditional application security tools often operate as isolated firewalls or separate dashboards that developers rarely look at until an alert fires. This creates friction between engineering and security teams.
By embedding veguard.pro into your automated toolchain—starting with GitHub Actions—you shift security left. Environmental anomalies, unverified virtual machines, and compromised runner configurations can be flagged or blocked before code merges or assets deploy to production.
Setting Up Vegaurd.Pro in GitHub Actions
Adding veguard.pro to your workflow is designed to be lightweight and zero-friction. Using our standard API hooks and custom action scripts, you can configure your pipeline YAML files to query device risk scores during key build or authentication stages.
Here is a quick look at how teams configure their workflow integration:
1. Trigger on Push or Pull Request: Initiate automated validation checks whenever code changes target protected branches.
2. Run Hardware Trust Assessment: Query veguard.pro endpoints to evaluate runtime execution footprints and hardware signatures.
3. Conditional Gate Enforcement: Automatically pass or fail builds based on pre-set, role-based device trust thresholds.
Boosting Velocity Without Compromising Safety
The goal of workflow automation isn't to slow developers down with manual approvals; it's to eliminate human error and catch structural risks instantly. By plugging veguard.pro into your CI/CD stack, your team maintains total visibility into device integrity with zero manual oversight.
Ready to Secure Your Pipeline?
Bring robust hardware-level intelligence into your engineering toolchain today. Visit veguard.pro to access our developer documentation and start your integration in minutes.
🌐 veguard.pro