what if autonomous multi-cloud security meshes replaced static perimeter firewalls for next-gen application protection?
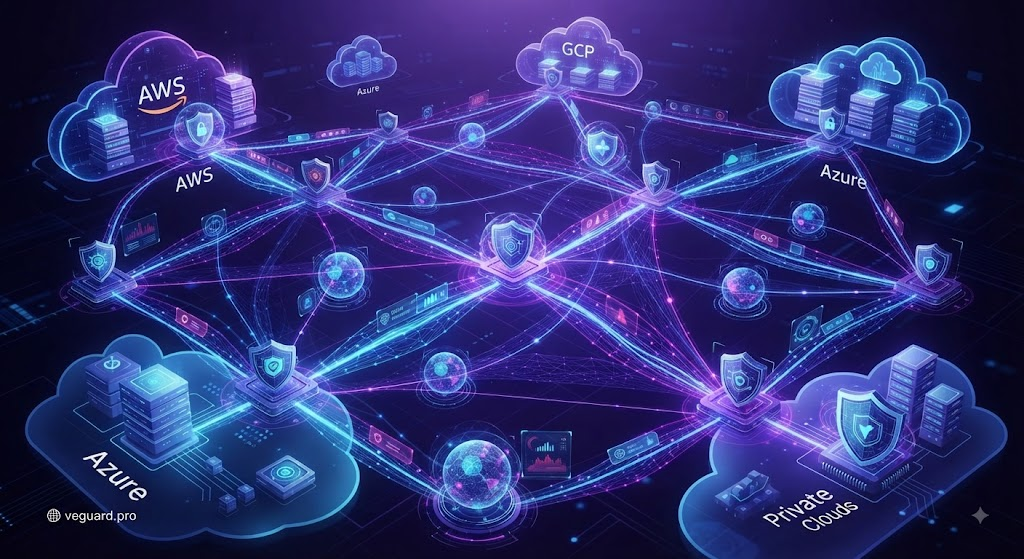
Beyond the Perimeter: The Rise of Autonomous Multi-Cloud Security Meshes
For as long as web applications have existed, security architecture has been shaped by the concept of a boundary. You built a wall around your data center—a perimeter firewall—and assumed that traffic inside the fence was safe. Today, that mental model is broken.
Modern engineering teams deploy microservices across AWS, Google Cloud, and Azure, routing requests through global CDNs and serverless edge functions. In this fragmented, borderless landscape, what happens to traditional security? What if static perimeter defenses were entirely replaced by autonomous multi-cloud security meshes driven by real-time hardware trust?
The Collapse of the Static Perimeter
As applications become distributed, attackers have adapted. They no longer need to breach a physical server room; instead, they exploit the gaps between multi-cloud services using automated scripts, residential proxy rotation, and stolen session tokens.
Static IP blacklists and custom regex rulebooks cannot keep up with this dynamic threat surface. Maintaining separate security configurations across multiple cloud providers creates blind spots, engineering overhead, and inevitable human error.
Enter the Autonomous Security Mesh
Imagine a security architecture where trust is not bound by network location or IP addresses, but anchored directly to the physical device and execution environment of the client.
In an autonomous multi-cloud security mesh:
- Decentralized Enforcement: Trust policies travel with the request, evaluated instantly whether the traffic lands on an AWS instance, a Cloudflare edge worker, or a Google Cloud container.
- Hardware-Level Validation: Instead of trusting static credentials or cookies, the mesh verifies physical device entropy, hardware clock telemetry, and behavioral consistency in real time.
- Self-Healing Adaptation: Threat signals detected in one cloud region instantly propagate across the entire mesh, neutralizing automated botnets globally within milliseconds.
Veguart.pro and the Future of Distributed Trust
Building this future requires a unified language of device trust. Veguart.pro is designed from the ground up to fit into distributed environments. By generating dynamic, hardware-bound trust scores that integrate natively across your entire infrastructure stack—from CI/CD pipelines to serverless edge nodes—we help organizations eliminate blind spots.
Security shouldn't be fragmented just because your cloud infrastructure is. By shifting toward hardware-backed device trust across all deployment targets, engineering teams can achieve true resilience.
Step Into the Future of Security
The perimeter is gone, but application protection is entering an era of unprecedented intelligence. Are you ready to transition from static firewalls to dynamic device trust?
Explore how veguard.pro empowers modern multi-cloud architectures with autonomous, hardware-bound security at veguard.pro today.
🌐 veguard.pro