decoding the edge: how veguard.pro intercepts script injection before it touches origin servers
Behind the Edge: How veguard.pro Intercepts Threats Before Origin
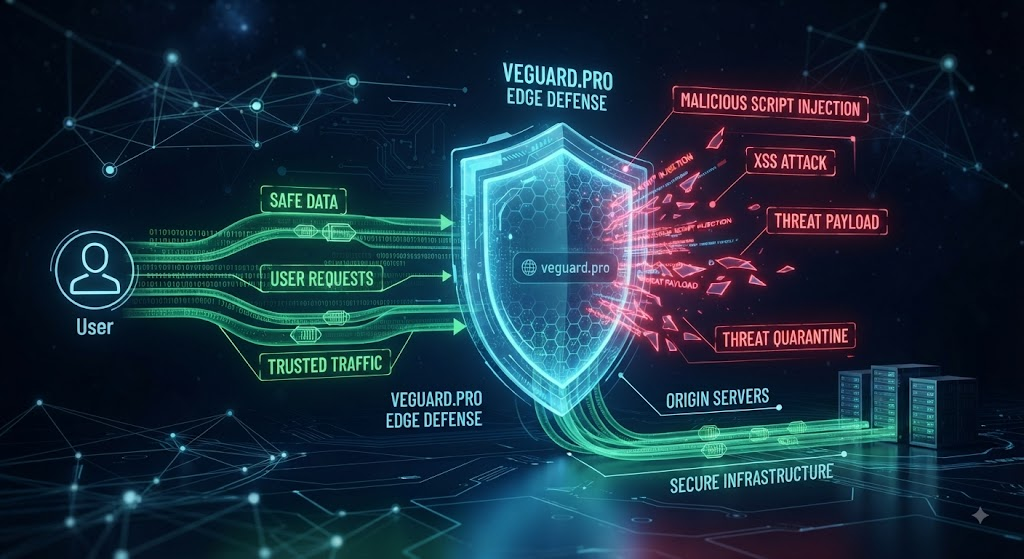
When building modern web applications, developers spend countless hours optimizing database queries, microservices, and backend logic. Yet, security is often left reactive—waiting for malicious traffic to arrive at the origin server before a Web Application Firewall (WAF) or backend script makes a judgment call. By then, valuable CPU cycles have been wasted, and exposure risks have multiplied. Today, we are taking you behind the scenes to see how veguard.pro handles incoming traffic entirely at the network edge.
The Journey of a Request: Edge vs. Origin
Traditional security models rely heavily on backend validation. A user sends a request, it traverses your cloud provider's network, wakes up your application container, queries middleware, and finally runs through validation logic. If the request contains a malicious script injection or payload manipulation, your server has already expended resources processing it. veguard.pro flips this model on its head by deploying intelligent device and payload verification directly to edge nodes worldwide.
Decoding the Real-Time Interception Pipeline
When a request hits a veguard.pro edge location, multiple security layers execute simultaneously in microseconds. First, the request's hardware-level device signature and execution footprint are evaluated. Second, payload heuristics check for hidden anomalies or obfuscated injection strings. Because this happens at the perimeter, blocked threats never consume a single cycle of your origin server's CPU. Your infrastructure stays lean, and your backend remains completely insulated from automated exploit sweeps.
Unlocking Seamless Protection Without Latency
Shifting security to the edge doesn't mean sacrificing speed. By utilizing optimized distributed computing, veguard.pro evaluates risk indicators instantaneously, ensuring legitimate users experience lightning-fast load times while malicious actors are dropped before handshake completion. It is a smarter, quieter way to safeguard your digital assets.
Secure Your Application Today
Stop letting junk traffic and script injections drain your backend resources. Discover how veguard.pro’s edge-native security infrastructure can protect your platform. Visit veguard.pro to get started today!
🌐 veguard.pro