securing high-value creator payout settings: stopping malicious cookie-hijacking cookie-swaps before earnings withdrawal
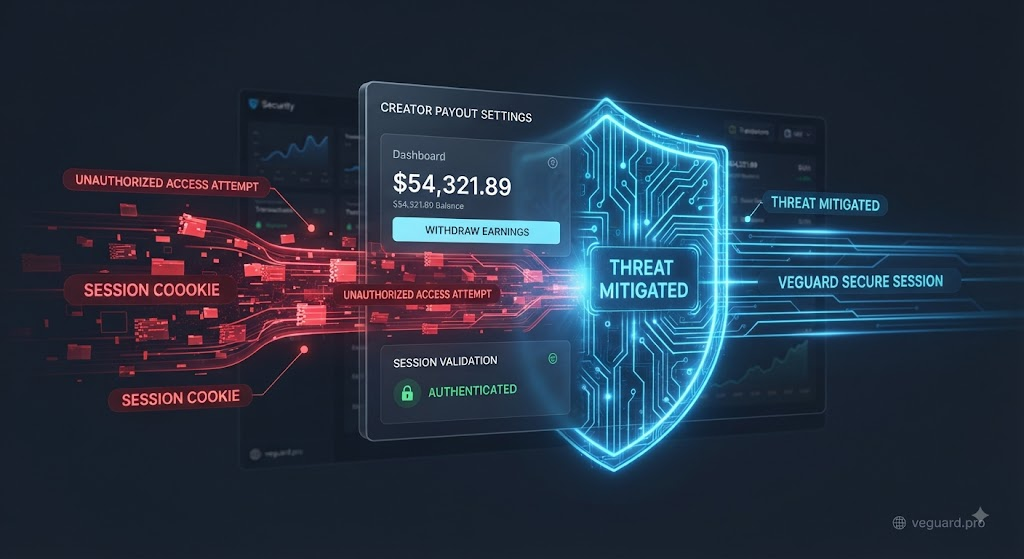
Securing Creator Payouts: How Hardware-Bound Trust Stops Session Hijacking
The creator economy thrives on trust. Creators spend countless hours building audiences, producing content, and driving engagement, relying on platform dashboards to safely disburse their earnings. However, this financial pipeline has become a prime target for sophisticated cybercriminals using session hijacking and cookie-swapping techniques.
The Vulnerability of Traditional Sessions
When a creator logs into a platform, standard architectures issue a session cookie. If an attacker manages to steal this cookie via infostealer malware, malicious browser extensions, or XSS vectors, they inherit an authenticated session. Because the attacker appears to be logged in from an authenticated browser, standard security layers like SMS or authenticator-app MFA are often completely bypassed.
Once inside, the attacker navigates straight to the payout settings, replaces the bank account or crypto wallet address with their own, and initiates a withdrawal. By the time the creator realizes what happened, the funds are gone.
The Flaw in Static IP and Cookie Rules
Traditional fraud mitigation relies heavily on IP reputation checks or basic geo-location tracking. But modern attackers use residential proxies that match the creator's usual city or neighborhood, completely blinding simple IP-filtering tools. Relying purely on software-layer cookies leaves platforms vulnerable because cookies can be easily copied, exported, and replayed.
Stopping Fraud at the Hardware Edge with veguard.pro
veguard.pro solves this problem by shifting from fragile software tokens to hardware-bound device intelligence. Instead of just trusting a cookie, veguard.pro evaluates low-level browser execution characteristics, hardware clock timing metrics, and persistent device fingerprints.
When a sensitive action—such as modifying financial payout settings—is triggered, veguard.pro cross-references the current execution footprint with the trusted hardware token established at login. If an attacker attempts to execute a payout swap from a cloned cookie running on a foreign machine, the risk engine flags the anomaly instantly, locking the settings change and alerting security teams.
Conclusion
Protecting your platform's creators means protecting their financial livelihood. By integrating veguard.pro's real-time edge security, you remove the blind spots of session hijacking and ensure that only verified hardware owners can touch sensitive account configurations.
Ready to secure your marketplace payouts? Visit https://veguard.pro to get started today.
Call to Action: Stop financial fraud before it hits your ledger. Schedule a technical walkthrough with veguard.pro today.
🌐 veguard.pro