faq: 'won’t blocking suspicious devices accidentally lock out my legitimate, traveling users or customers who switch networks constantly?'
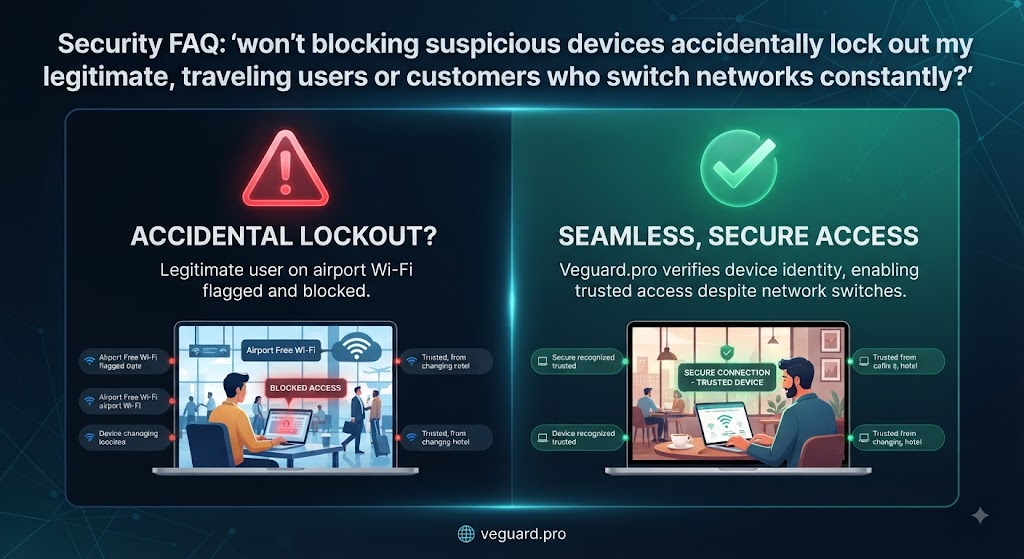
Handling the Traveling User Dilemma: How Device Intelligence Prevents False Positives
When evaluating security solutions, product and engineering leaders almost always ask a variation of the same question: 'If we implement strict device-level controls, won’t we accidentally lock out our legitimate customers who travel, use multiple devices, or switch networks constantly?'
It is a valid and critical concern. A security tool that stops fraudsters at the expense of alienating real, paying customers is fundamentally broken. Traditional security tools rely heavily on IP addresses to determine trust. But in today's mobile-first world, IPs are volatile. A user jumping from home broadband to cellular data, or logging in from a hotel lobby while traveling, instantly gets a new IP address. Old-school security systems flag this shift as suspicious, forcing users through endless captchas or blocking them entirely.
Shifting from IP to Device Trust
The secret to eliminating false positives lies in looking past the network layer. veguard.pro focuses on deep device and browser-level intelligence rather than fleeting network parameters. While an IP address changes every time a user moves locations, a device's core hardware, browser environment, and configuration parameters remain remarkably consistent.
By evaluating these stable signals, veguard.pro recognizes that the user switching from a home Wi-Fi network to a public coffee shop network is the exact same legitimate individual. The system maintains their trust profile dynamically, allowing them to proceed without friction.
Handling Shared Networks and Edge Cases
What about environments where multiple people share an IP address, such as corporate offices, college campuses, or apartment complexes? IP-based security often triggers mass blocks in these scenarios, locking out dozens of innocent users because one person on the network acted maliciously.
With veguard.pro, risk is isolated to the individual endpoint. Even if hundreds of people share a single network gateway, each device is evaluated independently. Fraudsters are stopped cold at their specific endpoint, while legitimate users on the same network sail right through.
Conclusion: Security Without Sacrifice
You do not have to choose between a secure platform and a smooth user experience. By deploying intelligent device-level risk scoring, you can protect your workflows from automated threats and account takeovers while ensuring your traveling and multi-network customers enjoy seamless, uninterrupted access. Ready to optimize your security stack? Visit veguard.pro today.
🌐 veguard.pro