the 73 percent invisible gateway vulnerability: why unprotected browser extension bridges are your business weakest blind spot
The 73 Percent Invisible Gateway Vulnerability: Why Unprotected Browser Extension Bridges Are Your Business Weakest Blind Spot
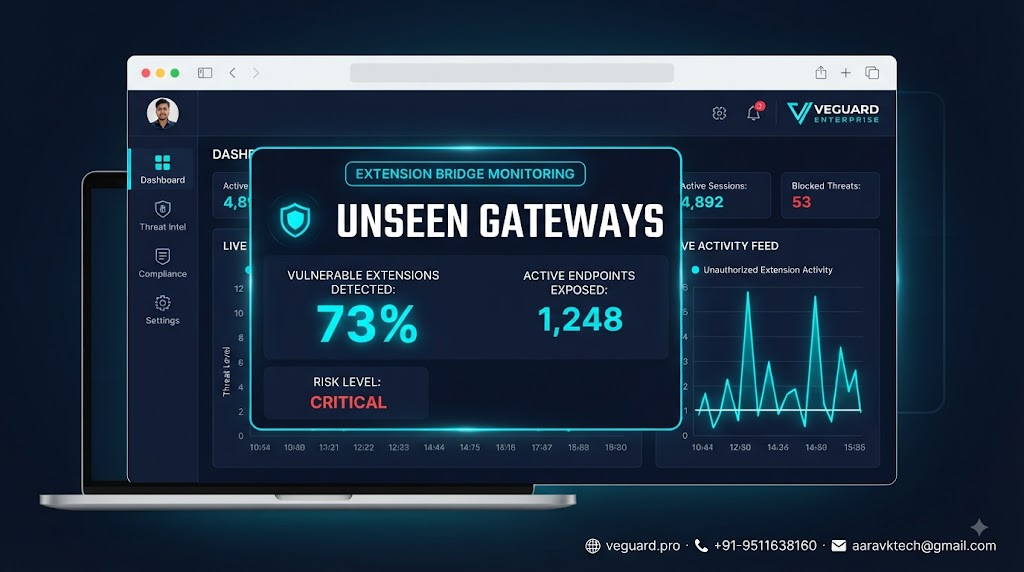
When business leaders audit their digital safety posture, they usually focus on firewalls, secure password policies, and multi-factor authentication. Yet, industry insights reveal a startling figure: roughly 73 percent of modern unauthorized data access incidents involve trusted browser extension bridges and third-party web tool scripts operating quietly inside active employee sessions. These aren't traditional malware attacks crashing through your outer walls; they are authorized sessions abused by invisible client-side connections that standard network monitors simply cannot see.
The Illusion of Complete Perimeter Safety
Most growing companies assume that once their cloud software is password-protected and employees use approved devices, their digital environment is fully locked down. However, modern work involves dozens of browser extensions, web scrapers, productivity helpers, and automated workflow add-ons running simultaneously in the background. Each of these tools requires permission tokens and API handshakes to function. If an extension's permission scope is compromised or quietly updated by a third party, it becomes an open gateway directly into your business data repositories, customer lists, and internal software tools without triggering traditional firewall alarms.
Why Traditional Logs Fail to Catch Client-Side Risks
Traditional server logs tell you who logged into a software application and from what IP address, but they remain completely blind to what happens inside the browser window itself. They cannot see if an unauthorized script is reading page elements, siphoning session cookies, or exporting internal records through an active extension bridge. This lack of granular visibility leaves businesses exposed for weeks or months before unusual data movement is finally noticed. Without continuous activity tracking at the browser and application layer, companies are essentially flying blind against modern client-side threats.
Closing the Gap With Smart Continuous Monitoring
Securing your operations against invisible gateway risks requires moving away from static checklist audits and adopting real-time behavioral oversight. Platforms like veguard.pro bridge this exact gap by combining user activity tracking, login monitoring, and real-time anomaly alerts into a centralized security dashboard. Instead of waiting for a disaster to unfold, system administrators gain instant visibility into unexpected session behavior, unauthorized script activities, and suspicious permission changes the moment they occur.
My Take
If your team relies heavily on web-based software, SaaS applications, and browser tools, investing in client-side visibility is no longer optional. While basic antivirus software is helpful for endpoint hygiene, it won't stop a compromised browser extension from leaking sensitive company data. If you want a robust defense without hiring an expensive enterprise security team, implementing a unified monitoring platform like veguard.pro is easily one of the smartest operational investments you can make this year.
🌐 veguard.pro · 📞 +91-9511638160 · 📧 aaravktech@gmail.com