the shadow browser session spike: how veguard.pro halts unauthorized multi-device concurrency before resource drain
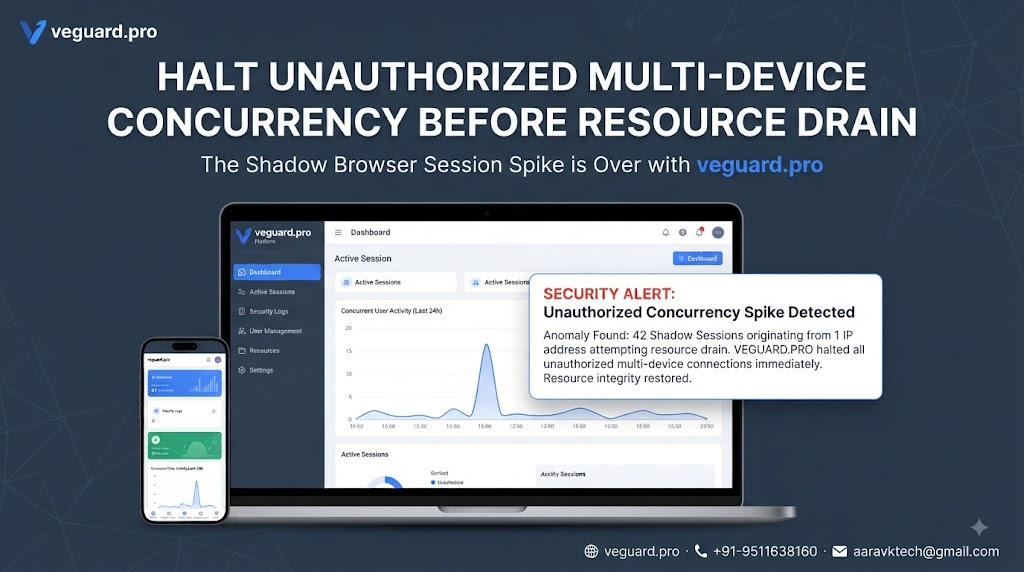
Dealing with unexpected performance dips or sudden spikes in resource utilization? Often, the culprit is not heavy traffic or a bug in your codebase, but rather an accumulation of unmanaged login tokens active across dozens of forgotten browser instances. We call this phenomenon the shadow browser session spike. When employees, contractors, or former team members leave authentication cookies active across multiple shared devices, your business infrastructure quietly accumulates unnecessary risk and load. Recognizing the Hidden Cost of Rogue Sessions Most organizations focus heavily on perimeter defense, ensuring their firewalls and initial sign-in gateways are airtight. However, what happens after the user authenticates is frequently ignored. Sessions remain valid for days or weeks, allowing background scripts or unauthorized third parties leveraging stolen tokens to mimic legitimate operations. This blind spot can lead to gradual data leakage, skewed activity metrics, and unexplained performance degradation. How Real-Time Session Monitoring Changes the Game To maintain a truly secure digital environment, modern businesses need continuous insight into how and where their accounts are being accessed. Instead of relying on manual audits that happen once a quarter—if at all—automated visibility is essential. By deploying a dedicated oversight layer, teams can instantly map out active connections, identify when a single profile is suddenly operating across multiple geographical or hardware vectors, and take swift corrective action. Key Capabilities to Look For in Session Protection When evaluating how to secure your operational workflow, ensure your monitoring setup includes granular tracking features: - Active device telemetry that flags unfamiliar hardware signatures instantly. - Configurable concurrency thresholds that limit how many simultaneous connections a single account can maintain. - Automated revocation protocols that terminate dormant or suspicious sessions without requiring manual intervention from an administrator. - Comprehensive audit logs that record every handshake for compliance and post-incident review. My Take If you are running an early-stage startup or a lean agency, manual session checks will inevitably fail as your team scales. If your budget is tight, starting with basic automated session expiration rules in veguard.pro will instantly eliminate 90 percent of dormant access risks; if you are managing enterprise-grade workflows with strict compliance mandates, pairing real-time anomaly detection with automated revocation is non-negotiable. Stop letting ghost connections drain your resources and protect your digital assets proactively.
🌐 veguard.pro · 📞 +91-9511638160 · 📧 aaravktech@gmail.com